Posts

Integrated Security

Integrated Security is Transforming the U.S. Homeland

The U.S. security services market, valued at $48.8 billion, is undergoing a fundamental shift. Organizations are no longer viewing physical security, investigations, and cyber defense as separate functions—they are increasingly integrated into a unified approach to risk management.

By Frank Costa, President, Nexgen Protection Services — Integrated Security 

This integration provides several advantages:

  • Holistic threat detection: Combining physical and cyber intelligence allows organizations to identify vulnerabilities that might otherwise go unnoticed.
  • Faster incident response: Coordinated teams can act immediately across multiple domains, reducing the impact of both physical and digital threats.
  • Streamlined investigations: Unified data and reporting systems improve the efficiency and effectiveness of post-incident analysis.

As threats evolve, from cyber intrusions to insider risks and physical breaches, clients are demanding security solutions that are proactive, comprehensive, and interoperable. Providers that can seamlessly merge these disciplines are capturing market share and redefining industry standards.

For businesses, the takeaway is clear: investing in integrated security is no longer optional. The most effective strategies combine technology, personnel, and intelligence to anticipate, deter, and respond to risks across every potential front.

The transformation of the $48.8 billion security market reflects a broader truth: in today’s complex threat environment, security works best when it works together.

Reference (APA):
IBISWorld. (2026). Security services in the US: Market research report.

#SecurityIndustry #IntegratedSecurity #RiskManagement #CyberSecurity #PhysicalSecurity #Investigations #BusinessContinuity #ThreatPrevention #CorporateSecurity #SecurityTrends
Security with Awareness Training

Boost Security with Awareness Training

By Frank Costa, President, Nexgen Protection Services – Awareness Training

Human error remains one of the leading causes of security breaches and operational risks. Even the most advanced systems can be undermined if employees aren’t prepared to recognize and respond to threats.

Security awareness training addresses this gap by equipping teams to:

  • Identify risks early – recognizing suspicious activity or potential breaches before they escalate.
  • Follow proper protocols – ensuring consistent, effective responses across the organization.
  • Respond confidently under pressure – minimizing mistakes and reducing the impact of incidents.


A well-trained workforce is more than just a line of defense—it strengthens the entire security ecosystem, supporting technology, procedures, and leadership in safeguarding people, assets, and data.

Investing in ongoing awareness training ensures your team remains up to date with evolving threats, emerging tactics, and best practices. The result is a proactive, resilient security culture that turns potential vulnerabilities into points of strength.

Security is not just about tools and policies—it’s about people who are ready, aware, and capable of acting decisively when it matters most. Build a team that recognizes risks early and responds with confidence and precision.


Reference (APA):
Hadnagy, C. (2022). Social engineering: The science of human hacking (2nd ed.). Wiley.

#SecurityAwareness #RiskManagement #CyberSecurity #OperationalRisk #EmployeeTraining #SecurityCulture #ThreatPrevention #CorporateSecurity #HumanError #SecurityStrategy

Overnight Patrols

Overnight Patrols Keep Communities Safe

Maintaining safety isn’t a 9-to-5 job—criminal activity doesn’t sleep, and neither does proactive security. That’s why conducting active overnight security patrols is essential for protecting communities and businesses.

By Frank Costa, President, Nexgen Protection Services – Overnight Patrols 

These patrols serve a dual purpose:

  • Visible presence: The sight of uniformed personnel and marked vehicles acts as a strong deterrent to potential offenders.
  • Rapid intervention: Should an incident occur, patrol teams can respond immediately, minimizing potential damage or loss.

Nighttime patrols are a cornerstone of modern security strategy. They help reduce risks, reassure residents, and maintain continuity of operations for businesses located in areas vulnerable to crime. By keeping eyes on the ground while the community rests, security teams help ensure a safer environment for everyone.

The effectiveness of overnight patrols depends on trained personnel, well-planned routes, and regular communication with monitoring teams. When combined with technology—like CCTV and alarm systems—the impact is amplified, creating a layered security approach that addresses both prevention and response.

In short, security works best when it’s proactive, visible, and continuous. Overnight patrols are not just about monitoring—they are about keeping communities safe, preventing incidents before they happen, and providing peace of mind to those who live and work in the area.

Reference (APA):
Fennelly, L. J. (2022). Effective physical security (6th ed.). Butterworth-Heinemann.

#Security #PhysicalSecurity #RiskManagement #CommunitySafety #Patrol #CrimePrevention #BusinessSecurity #ThreatDeterrence #SecurityStrategy #OvernightPatrols

Understanding FPCON: A Critical Security Framework

Understanding FPCON: A Critical Security Framework

By Frank Costa, President, Nexgen Protection Services — FPCON: A Critical Security Framework

In today’s evolving threat landscape, understanding how the U.S. protects its people and facilities is more important than ever. One key system used across military installations and government environments is the Force Protection Condition (FPCON). A critical security framework. 

FPCON is a standardized system developed by the U.S. Department of Defense to assess and respond to terrorist threats against personnel and facilities. It provides commanders with a structured framework to adjust security measures based on real-time intelligence and risk levels. 

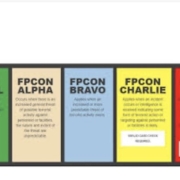
The system operates across five escalating levels: Normal, Alpha, Bravo, Charlie, and Delta. As threat levels increase, so do security measures—from routine ID checks and random inspections to full lockdown scenarios with restricted access and heightened armed presence. 

What makes FPCON especially effective is its proactive design. It doesn’t just respond to threats—it helps deter, detect, delay, and defend against potential attacks before they occur. 

For businesses operating near military bases, government facilities, or critical infrastructure, awareness of FPCON levels is essential. Sudden changes can impact access, logistics, employee movement, and overall operations.

In a world where threats can evolve rapidly, FPCON  is a critical security framework that underlines a broader truth: security is not static. It’s dynamic, intelligence-driven, and requires constant adaptation.

Organizations that understand and align with these systems are better positioned to protect their people, assets, and continuity.

Reference (APA):
Military.com. (2025). Force Protection Condition (FPCON) levels explained.

#SecurityAwareness #FPCON #RiskManagement #CorporateSecurity #ThreatIntelligence #BusinessContinuity #HomelandSecurity #PhysicalSecurity #SecurityIndustry #Leadership

Rising U.S. Threats Amid Iran Conflict

Rising U.S. Threats Amid Iran Conflict

By Frank Costa, President, Nexgen Protection Services — Rising U.S. Threats 

The evolving Iran-region conflict is no longer a distant geopolitical issue—it is actively shaping the threat environment inside the United States.

According to the Department of Homeland Security (DHS), ongoing tensions have created a heightened threat landscape, with increased risks spanning both cyber and physical domains. Pro-Iranian cyber actors and hacktivist groups are expected to conduct attacks against U.S. networks, ranging from disruption to more targeted operations. 

At the same time, DHS warns of a more unpredictable danger: individuals or small groups within the U.S. who may become inspired by overseas events. These actors can mobilize quickly, often without direct coordination, making them harder to detect and prevent. 

Recent large-scale strikes in early 2026 have only intensified these risks. Cyber incidents linked to Iran-aligned groups and rising concerns about retaliatory activity highlight how global conflict increasingly translates into domestic exposure. 

For businesses and security leaders, this shift is critical. The line between international conflict and domestic risk is thinner than ever. Organizations must strengthen cyber defenses, monitor threat intelligence, and prepare for a broader spectrum of potential incidents—from digital disruption to ideologically motivated violence.

The takeaway to rising U.S. threats is clear: geopolitical awareness is now a core component of enterprise security strategy. What happens overseas can—and increasingly does—impact operations at home.

Reference (APA):
U.S. Department of Homeland Security. (2025). National Terrorism Advisory System Bulletin: Summary of the threat to the United States.

#SecurityThreats #CyberSecurity #RiskManagement #HomelandSecurity #ThreatIntelligence #BusinessContinuity #NationalSecurity #CorporateSecurity #Geopolitics #2026Trends

Border Security Risks Are Rising in 2026

Border Security Risks Are Rising in 2026

By Frank Costa, President, Nexgen Protection Services

Boarder Security Risks

Violence near the U.S.–Mexico border is escalating in ways that demand urgent attention from businesses, security leaders, and policymakers alike.

Criminal organizations are no longer relying solely on traditional tactics. Increasingly, they are deploying advanced methods—such as drone-dropped explosives and improvised explosive devices (IEDs)—to expand their reach and capabilities. These developments signal a shift toward more sophisticated, asymmetric threats that were once largely confined to conflict zones.

For organizations operating in border states or along key supply chain corridors, the implications are serious. The security risk is no longer isolated—it has the potential to spill over into U.S. communities, impacting personnel safety, logistics, and overall business continuity.

This evolving threat landscape requires a more proactive and intelligence-driven approach to security risk assessment. Companies should reassess risk exposure, strengthen coordination with local and federal authorities, and ensure that their security partners are equipped to respond to emerging, high-impact scenarios.

Preparedness is no longer optional—it’s a strategic necessity.

Reference (APA):
Congressional Research Service. (2025). Mexico: Organized crime and drug trafficking organizations.

#BorderSecurity #RiskManagement #SecurityThreats #ExecutiveProtection #BusinessContinuity #CorporateSecurity #SupplyChainRisk #SecurityIndustry #ThreatIntelligence #2026Trends

Security Gaps

Spotting and Shutting Security Gaps in Healthcare

Spotting and Shutting Security Gaps in Healthcare Visitor Management

Frank Costa, President, Nexgen Protection Services

Hospitals and healthcare facilities are facing an increasingly complex risk landscape — from unauthorized access and patient privacy breaches to workplace violence and operational disruptions. In this environment, identifying security gaps before an incident occurs can make all the difference.

Visitor management is a critical frontline defense. Every person who enters a facility — whether a patient, family member, contractor, vendor, or volunteer — represents a potential point of vulnerability. Without proper procedures, bad actors or accidental breaches can compromise safety, privacy, and compliance.

ASIS International emphasizes that robust visitor management systems integrate credentialing, access control, monitoring, and audit trails to reduce risk and ensure accountability (ASIS International, 2020). Effective systems not only track who is in the facility but also help identify unusual patterns or behaviors that may indicate a security threat.

Practical strategies for healthcare security leaders include:

  • Implementing pre-registration and verification for all visitors
  • Using ID badges, wristbands, or digital credentials tied to access levels
  • Monitoring entrances and high-risk areas with video and patrols
  • Maintaining audit logs and regular reviews to detect anomalies
  • Training staff to recognize and escalate suspicious behavior

By proactively closing security gaps in visitor management, healthcare organizations protect patients, staff, and sensitive data, while maintaining a safe and welcoming environment. Security is not just about responding to incidents — it’s about anticipating risk and building trust through vigilance.


Reference (APA 7th ed.)
ASIS International. (2020). Healthcare security guidelines: Visitor management and access control. ASIS International.

#HealthcareSecurity #VisitorManagement #SecurityProtection #RiskManagement #PatientSafety #OperationalResilience #HospitalSecurity #AccessControl #SecurityLeadership #WorkplaceSafety


Team

Teamwork Is Your Greatest Security Protection

By Frank Costa, President, Nexgen Protection Services

In high-risk or hostile environments, technology and procedures matter — but nothing protects you more than knowing your team has your back. Physical barriers, surveillance systems, and access controls are critical, yet the human element — trust, coordination, and mutual support — is often the most effective layer of protection.

Security professionals, whether in corporate settings, critical infrastructure, or executive protection, thrive when teams operate with shared awareness, clear communication, and mutual accountability. Each member becomes a force multiplier, capable of identifying risks, responding quickly, and keeping others safe.

ASIS International emphasizes that effective security programs integrate people, process, and technology — and that human factors, including teamwork and situational awareness, are essential to protecting assets and personnel (ASIS International, 2021). Psychological safety, trust, and shared responsibility are not optional; they are operational imperatives.

Practical ways to strengthen your team’s protective capability include:

  • Conducting joint training and drills to build coordination under pressure
  • Maintaining open channels for reporting risks or anomalies
  • Encouraging mutual accountability and proactive assistance
  • Supporting one another physically and psychologically in challenging environments

Remember: security is as much about people as it is about systems. Looking out for each other is a force multiplier. In any high-risk scenario, the confidence that your team will act decisively and responsibly is the greatest protection you can have.

Reference (APA 7th ed.)
ASIS International. (2021). Security management professional standards. ASIS International.

#CorporateSecurity #SecurityProtection #Teamwork #SituationalAwareness #WorkplaceSafety #RiskManagement #OperationalResilience #ProtectAndServe #SecurityLeadership #MutualSupport


Security Protection

Who’s Really Inside Your Building? Rethinking Security Protection

By Frank Costa, President, Nexgen Protection Services

Take a moment and think about it. Not just the employees you see every day, but everyone who passes through your doors: cleaners, delivery drivers, contractors, IT support, facilities teams, visitors, temporary staff, and suppliers. How many of them were inside your building today — and how well do you really know them?

Physical security isn’t just about locking doors or staffing a front desk. It’s about understanding and managing access risk across all personnel. Every individual who enters your facility represents a potential vulnerability — from accidental safety oversights to deliberate threats.

ASIS International emphasizes that comprehensive security protection programs account for all building occupants, integrating access control, identity verification, and monitoring procedures to mitigate risk while maintaining operational flow (ASIS International, 2021). This includes temporary personnel, vendors, and service providers, whose presence is often overlooked in standard security planning.

Best practices include:

  • Vetting and credentialing all personnel with access to sensitive areas
  • Implementing time-bound or role-based access controls
  • Monitoring entry points and activity through surveillance and audit logs
  • Conducting regular reviews of visitor and contractor access policies

By thinking beyond employees, security leaders can reduce blind spots, strengthen operational resilience, and protect both people and assets. Security is not just a policy — it’s an awareness that every individual matters.

Reference (APA 7th ed.)
ASIS International. (2021). Physical security professional standards. ASIS International.

#CorporateSecurity #SecurityProtection #AccessControl #RiskManagement #PhysicalSecurity #SecurityAwareness #EnterpriseRisk #VisitorManagement #OperationalResilience #WorkplaceSafety


Privacy

Bug Sweeps: Protecting Privacy and Securing What Matters

By Frank Costa, President, Nexgen Protection Services

In a world where information is a high-value asset, bug sweeps have become an essential tool for safeguarding privacy, securing sensitive data, and providing peace of mind. Whether you’re an individual protecting your personal space or a business defending proprietary information, the risks of unauthorized surveillance are real and growing.

Bug sweeps detect hidden microphones, cameras, GPS trackers, and other covert devices that can compromise personal or corporate security. By proactively identifying vulnerabilities, individuals and organizations can prevent espionage, data breaches, and reputational damage before they occur.

According to ASIS International, systematic technical surveillance countermeasures (TSCM) — commonly known as bug sweeps — are a best practice in both corporate and executive protection programs (ASIS International, 2019). TSCM services combine specialized equipment, trained personnel, and methodical inspection processes to uncover threats that are otherwise invisible.

For businesses, bug sweeps protect intellectual property, trade secrets, client information, and sensitive strategic plans. For individuals, they provide assurance that private conversations, meetings, or personal activities remain confidential. Beyond protection, bug sweeps foster a culture of vigilance — demonstrating that privacy and security are priorities.

In an era of increasingly sophisticated surveillance, proactive detection is far better than reactive response. Investing in bug sweeps isn’t just about mitigating risk; it’s about preserving trust, integrity, and operational confidence.

Reference (APA 7th ed.)
ASIS International. (2019). Technical surveillance countermeasures (TSCM) standard. ASIS International.

#PrivacyProtection #BugSweeps #TechnicalSurveillanceCountermeasures #CorporateSecurity #ExecutiveProtection #DataSecurity #InformationSecurity #RiskManagement #SecurityAwareness #ProtectWhatMatters